THE NEWS IN BRIEF
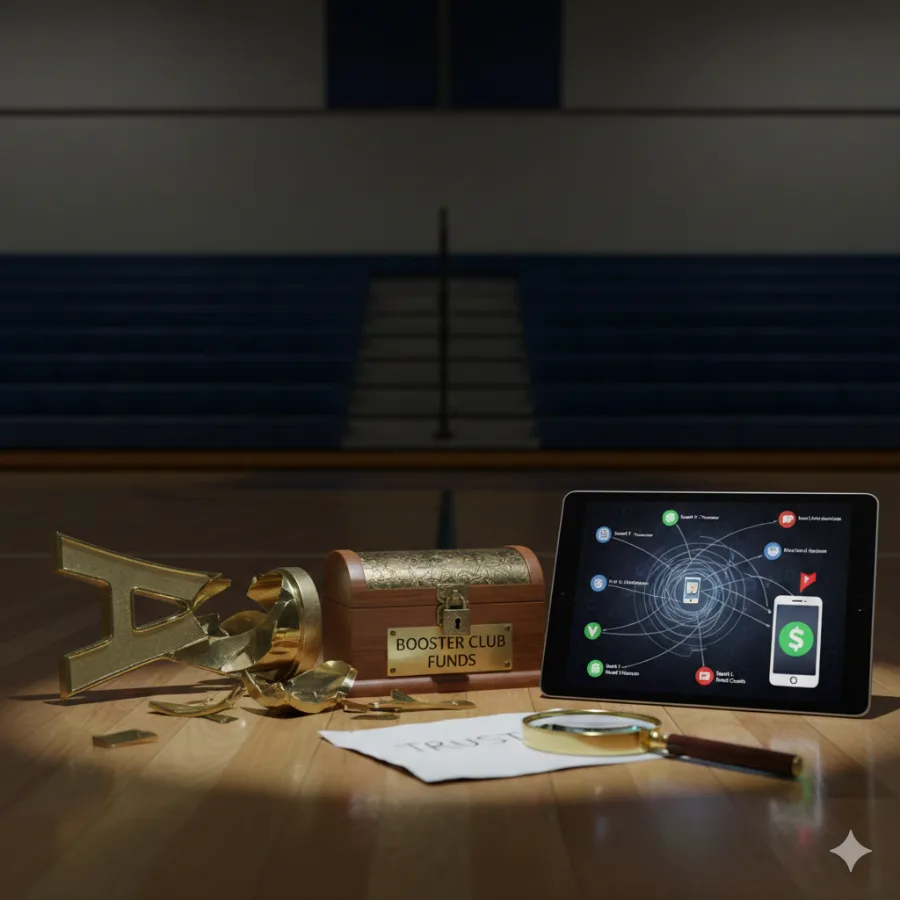
A Mason High School parent was sentenced to probation after being convicted of telecommunications fraud and theft from a school booster nonprofit. This incident exposes how easily trusted insiders can exploit the utter lack of financial segregation and oversight in organizations that run on “good faith” rather than rigorous controls.
THE CONSULTANT’S VERDICT
Let’s stop pretending this is just a local news story about a petty thief at a high school. This is a microcosm of the exact governance failure plaguing multi-national corporations from Riyadh to Toronto. The “Booster Club Syndrome” is rampant in the corporate world. You have a decentralized unit—a remote sales office, a specific project team, or an employee welfare fund—operating with autonomy because headquarters views the dollar amounts as immaterial. You operate on trust. You assume that because someone is a “parent” (or in your case, a tenured manager), they are ethical. This assumption is the cancer of internal audit.
In my fifteen years working across the GCC and North America, I have seen this exact dynamic destroy reputations. In Saudi Arabia, it often manifests through blind trust in family names or tenured expatriates; in Canada, it hides behind polite passivity. The mechanism is identical: a lack of Segregation of Duties (SoD) combined with digital access. The perpetrator here used “telecommunications fraud,” likely meaning unauthorized digital transfers. In your company, this is the regional manager using the corporate credit card for personal luxuries or manipulating the petty cash app, knowing full well that Internal Audit only samples transactions over a certain materiality threshold.
We must look at this through the lens of the IIA Global Internal Audit Standards, fully effective as of January 2026. Specifically, Domain IV (Managing the Internal Audit Function) demands that we assess risks dynamically. If you are ignoring low-value entities because they don’t hit a quantitative materiality score, you are failing the qualitative risk assessment required by the new Standards. Fraud in small units is not about the money lost; it is a barometer for the ethical culture of the organization. If a parent can steal from a booster club, your “trusted” branch manager can and will steal from you if the control environment is equally lax.
The sentencing to probation is a slap on the wrist, but the reputational damage to the nonprofit is permanent. Corporations face the same fate. When a small subsidiary is caught in a fraud scandal, the market does not care that the amount was small; they care that the parent company had no idea what was happening. This is a failure of oversight, pure and simple. You cannot audit trust. You must audit the controls that replace trust. If your audit plan for 2026 still relies on cyclical rotations that ignore these “low risk” pockets, you are not an auditor; you are a historian waiting to document a disaster.
THE RARE METHODOLOGY: The “Zero-Trust” Micro-Entity Stress Test
Stop wasting time with random sampling on low-risk entities. Implement the “Zero-Trust” Micro-Entity Stress Test. This is a high-intensity, algorithmic approach where you select the smallest, least significant financial unit in your organization (e.g., a regional party fund, a small marketing project, or a dormant subsidiary) and subject it to a forensic-level audit usually reserved for massive investigations.
Instead of looking for material errors, you are looking for control override capabilities. Use data analytics to map every single digital transfer, no matter how small, against the authorized user’s behavioral profile. If a transaction occurs at an odd hour, or to a peer-to-peer payment platform, it is flagged. The goal is not to recover $500; it is to prove that the governance model in your decentralized units is non-existent. You then use these findings to force the Board to fund automated monitoring tools for 100% of transactions across all entities, removing the “trust” factor entirely.
FINAL CALL TO ACTION
Abolish the concept of “immaterial entities” in your audit universe immediately and deploy continuous monitoring on all decentralized accounts, or prepare to be blindsided by the insider you trusted the most.